“The protection of personal data is a fundamental right for all Europeans, but citizens do not always feel in full control of their personal data,” European Commission vice president and justice commissioner Viviane Reding said in a press statement on Wednesday.
She tabled “a single set of rules” which would be valid across the EU, instead of today’s directive which each member state must implement on its own. Reding said the new regulations would streamline operations across the continent and “will save businesses around €2.3 billion a year.” The European Parliament and Council of Ministers will now consider the proposals.
The new rules could come into force in three to four years, Cyril Pierre-Beausse, an attorney with the law firm of Allen & Overy in Luxembourg, told Delano. If implemented in its current form, he reckoned the Grand Duchy “will have to repeal its existing legislation” and “we will have to re-work the whole data protection system in Luxembourg.”
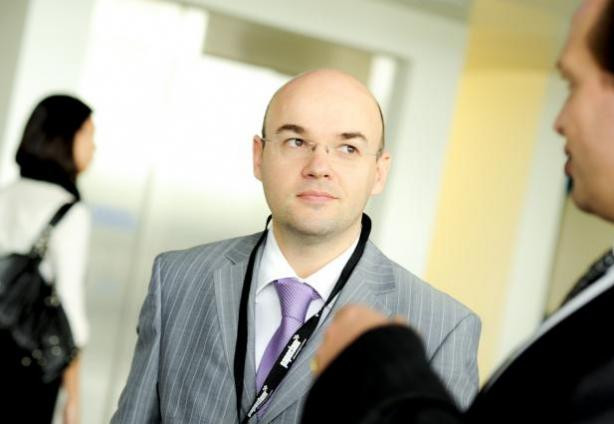
Today, internet-based services can obtain a passive opt-in from users, simply by posting a disclaimer that the use of their website implies consent to the company’s terms and policies, Pierre-Beausse (photo) explained. But Reding’s rules will require companies to explicitly state what user information will be gathered and exactly how it will be used, as well as obtain active agreement in advance.
For the first time, European privacy rules would apply to companies based anywhere in the world that attempt to market to customers within the EU, the attorney noted. That means, for example, European e-commerce players will no longer be at a competitive disadvantage compared to US sites, who currently only need to comply with America’s “less onerous” regulations.
In case of a data breach, companies would have 24 hours to notify their national data protection agency, such as Luxembourg’s CNDP, along with all the impacted customers. “In 24 hours, normally you just have had time to start the investigation and stop the leak,” Pierre-Beausse said. “Most companies are not prepared for that. For a small company, it will be very, very difficult.”
One other major change: the rules empower national data protection agencies to issue “severe sanctions” of up to two percent of worldwide turnover directly and on an administrative basis, instead of pursuing companies via the courts. Like the EU’s competition rules, the objective “is to make data protection a boardroom issue, to make it an element of corporate governance and this is very new.”
The draft EU rules, however, would not change the Luxembourg bank regulations that require all financial data to physically remain with the Grand Duchy’s borders, Pierre-Beausse explained.
It is possible the rules may be significantly changed by the time they are finalised. “There will be a huge amount of lobbying.... there will be lots of political debate, that’s for sure,” the attorney said.
“We support simplifying privacy rules in Europe to both protect consumers online and stimulate economic growth,” a Google Benelux spokeswoman told Delano. “It is possible to have simple rules that do both. We look forward to debating the proposals over the coming months.”